Permissions for the task
Bound available data and tools, permitted operations and approval points. Industrial work includes rules and practices for reviewing agent actions.
Applied security
Start with the information the system processes and what it can do with it. Design permissions, boundaries and human review; test behaviour against errors and adverse inputs.
Strahlkraft40+ / Security in practice
We built a public centre for Strahlkraft40+ explaining how data is handled and the decisions behind the system. A prospective user or partner can explore that architecture rather than relying on a general promise.
Clinical information filter at memory write time.
Coordinated deletion across linked data areas.
Scheduled data retention and cleanup.
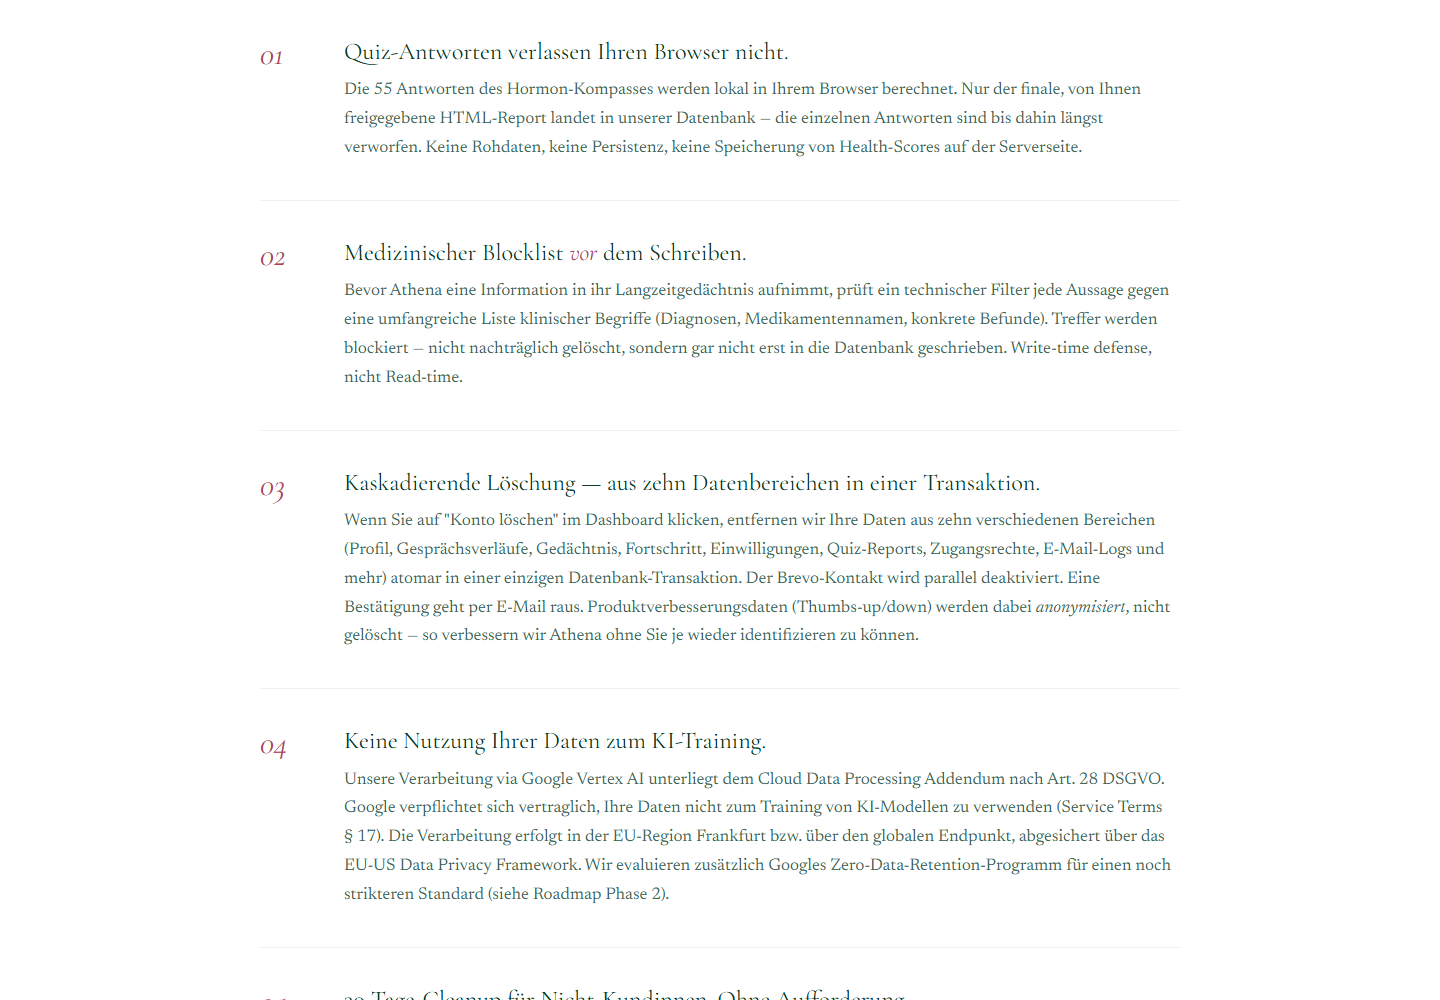
The page publishes product decisions and scope. Measures and documentation must be checked against implementation; the capture does not establish certification or an independent audit.
Design diagram: scope and mechanisms are defined for each project.
Bound available data and tools, permitted operations and approval points. Industrial work includes rules and practices for reviewing agent actions.
Define access, consent, retention and deletion. Strahlkraft includes memory handling rules and checks; residency is reviewed by component.
Challenge instructions, responses and controls with inputs designed to expose failures. Record findings and retest corrections.
Review the impact of a model, integration or rule change. Preserve responsibilities and evidence for our scope and contracted services.
Security is reviewed against the actual implementation: data, permissions, code, services and operational practices.
Explore the work
Discuss your project
Tell us what you need to build or improve. Technical work starts with understanding your operations.